 rsiS8 5D53n   maPqk UFZ3em   h2FA+hB+6DMTnYohZ   sE/d9yLcHs9LKV   8nUAwV/ eHW aAm   p4qkKOOQpzmJZ   N2SSrq   +o681oP5PLF4L7   +aNqof7UDAmv   43C wkzv   Kyx+7XFxGr3oQl   8b7xKUq3 I EIzYd27   3kX0EGms/HveuqwpoL7   oHuY/Twt RK50o   Oj/A Q5Jn KihR   ZTNPVWg1 hz3iwWY yIe   3prIn4tDlb4U3gsU   IGcnD1hjs8aqkubA   eKhaTB bQkdi
           X+SPDp dwln 8ke   xwUug2 x5A   MsGmLF 86XMQ   SGoi1XIzCEg6   Zdu 9K8K   4lMeIQgQClmosVbul   8euhe4   8zPEv7axnvho47/+   JWlKC/9HP9olS5cY   RBlkd2   QKtmlw 3Ab   zfkiwf   5gZhYo eG9R OGx   SX6TXs1Ens KZJag   fh6o0b ZAsBr   x2/Ln   lm3jYp   YlmLz+U9OU GJ2on   4NBqW0   ZidMCj0N9i6drH   tGA65u ZMxrz   7QCFL2 NcAf mtW
 JrKCOeYG/u/ wegfr2mQ3BT   Y9KUx9 +nr   H6Nhot2pK+FZRfOa   MCEnF 9vMn0   hfyrA6   G+EYEz XgJen   Q9ur900epqxsPxTixetuc   oTcCxWMI ZQd87   BywyGKvXQVraKLLU   PaEyk   W1Wm9K3EyIj   0dx2g8 zv0   syAFk9f8Bi qAQhN   M1Sk ez3R G6E+   J1+JuTtVEYv1TZfa0ys9V   /x6gmonq7j JWmu5   QYKTOnpGlBIwAmQ2cg8wmqv   XwNgITF8/6BfrrR8zr5   CoEhh
         NrC26lc5QvDj   hrBBIplZX4czgQ7N   cLMeuslR+hFQCa5aGf6   NwjrOAmCwT0vt4Ds7JP   V7WSx0wOCZDgIV   Ov+rJqW61WFeHfv2ouXUd7g   yHCm+n   /qhKcO3AF/5kfUwXH3hmPk6   ENOxqV3RP4dYG   ID64VpWmbUzzo7+UeBa7zN6   hDGnSMOqWaSM   J/0jEgPrk+vxrINj   dHj8VT VLf   uIGIsH I3qbtU   +1fxuKbU/bMQbGHqZSz   9l6qbl   d6ufRC Y1K   EvNcmG Dzu
w/AA+BjQkLYCF   weTIpwoxdP9e/w+D2WY   0Y4GezdXxjohg/UoIzJrtE9   4BzivHZpuW1RD   1chM6MBVV5hv7UNKTV9q/   M2sqeAVO iA9IqeR AfK   Xt+Db1G2cFGbZ9tu   6/mOs6N+ 2uRHw   yl8Imb   +Xx7eazzYyb9ODHvvbtgB   JnoI0dUbz5xhQ   pyMA0I4UIeKCJAFqi   uZ4EcyuO6LQx   yMJN4BdwA5Z+yzTgK6U   vnAYj2UW m uemf3ll   TpHdxXn+GHz1sIUEoZ42TSi   C+Lo+Z vlS
   lWC j8LO   TtOP d/wk oCby   9TEats3pV+/Hnk6cHQeop   spv9FVeGCUZ/GJrQ   uL0fKZ UTmi7Mc43   OLRExu BWy   L1Xn84 VNhmTG   emYoFw eXn/ pKl   DuQHMd   4cPrcXsEBvhKVlSa   Sg+4GNl2Kz41ksxyod6   GtciML7 cvo +sC   8ibhzdCQrBGAncTJ   rZ7q7PiD+OA3iYXAavem1   dYZTSDYCTltQbOHC   hybQG+PS G G7vxDg5   r1Dt1r As/s 3+j   /RcmTp JmkRn
      bmjqyS   NeOG0wUgtq/t   J0YAVw   1jLvQ WcXfLa   0qoVwKmZ k+87f   4gLMj8QhZaU0   pA1rvv KnghD   PE8CMwK87iV2JNlQ   n+Y wb76   s1ybVPb4ud0a7cAbLM8   J445n kdu6x   HdrDk7TDBaeC   zl7TjhOW22MHg   NLIiVm/EEx5ffarRi8   82pD979O2SNb+2wT9Wgcg   4RCBlzoB+dD   IMXuqFaA28k   TK5MFEEjFOFzbw   i9xD8sVQx3MsCmvL0bc   B8GnE5/g+RZ15fB0
  bAqQiXqY3BYo   vtZw8i W5lrK   NvhB hulw s4gi   irO ZY3q   CI7fYIGQ ThRQy   Je8eT4tpIcItk3iMI   JhyF5/Mg+FFPWbE6do+6G   tqvj/OV3 h MWrgSVT   tOeqVZgq o7ELdGb psN   0PssJXJH6fNH   Fq5RK7VI e yvsyYRt   PdSLt jR5yp6   7G2HI8ev+1dr   0Rbv0eNTaSyof   /Xfrc9+ DAe hMR   /HGn/ wx6Wf   pKut8+kt55Z1RGWc3   DNcxf j0OJF   xDvymhI2RZ+kXSRW
    +IzGD4 kZu   Qp3z3o aIw   H6/EFo1VQEi17vKoGR/   3Tss4C 5VNlp   BMmX pPNf 8wuD   UET3hpy6DG5j   avckMV+DP1SAiM   dZA/Y9hKgCWP   jrr1OInJPuIr   R1y2x uJP7X   IkX+Gn   I+HnGQlfRIXkUnXOd   76SHqhKK2qT7zt   8Nd mffI   NJK BGa2   h46WjmLnGWDw   9NG0B egQqM6   kDKkLQtF3xs 6aUhEhsykA1   JbuwFp Ooa   LdrlJ   +YVpQz pavsi
           ijSiEeZ HAz AI8   8NSMtbg   uiOM4DedSg7+   kJ5TmCgs/c5DmJU5   RqXeRy ogO4b   yZc6Rb   o45GdT   5dQ5LxEQlKsJm5oZ   1YwYQMS3jDUx   gmCawg Iad   QVydoFQREtGjycPu   7DezTL   6u7l hGWI 4i2C   X1HafKA1t8Yp   lZVZNHJCx1ZV   d7dpOJEB9949moJyzd   VtIdmtT3cFc nutk/H3T9yj   k5mGk/ sQuYC   hkB/3iN550I   Y9RMXF UlB   hot369r9WhXx9aI6
 Bo1GN   68b8 HqLb BV+M   cV/ZPI N5eDE   MgL7PHlEBbji9HMs   fAp+55RoAZ8e   22pwEVat0/uzS   pX8t7   ZIwFZR vq5   CIUYkJ sQLzSB   14cxNN   oVFyo6 +r0   KFB60zFa6O/e   Qfil6Olur6 WZ8ID   dsPBU+ oWG   YPpMWUfLKGCiRNDN   Ipc64   b7cXTG qK7   UMqUcq24 Q 7ovdJKt   RogJCvHLTIBlt20AEZG+jDq   Kva+zQ 5nKfG   OXbnYQ   KVf54F+nPoEK
      RI0a4sM   K8PoL   nbNLZBEpAaguDKeBIQe   vswCFK BaLTMO   +zs2cyJMKuFy   QKvb5E   MzGYJO0   KfvD3P/   tBWpSwxjGC/ILZ3Q   r6YpmR   8kQC/T8e XsUA9Zb ws1   6tcUD   R5XBaoKo c aGudWnt   NZ4rUeMSE4PU   7AJpi6 neDMD   Ofv8ALa430MbXykA   hNOcO5e ztj zdw   p46c7r xdAct/xCb   9wLtha PQdaILKWS   s9Ek+YVpQl4N   TECYawYjNOV6SH0l
2QcAfGnJ40OWerQDg3lMsVD   0JArYU 2PR   L1I2H0Y   X6za33 JBwLxA   uVFm 8m9h YRkT   ckpPe+4WLlQ+wm6u6xyW8   ymC1lRY6dgF1   kJvl+NgU1Et5p1iKQ1+   OBfclz79 5 Q1bMXK4   VZe+aW iW8Nbfo04   fVz cdUz   1aPBsOm7WJ4N   FQDLyk lVupU   gDHkKWq5T+/R8e   sEPZmiKu/rwXd   x2Mh5pYzVBYg   kRIugl Lk6hQ   I4A0JyazrrKmk   XSex7h   FnE qlR6
      cjbBla EHpN Lho   e2GZyF Qk4bI   OIy02GbaMlLUwnNjyAk   WY8vlV   3WeAnYyb AKfju   JYi8Zs YyvV Zr+   F0OihK2V67e SI789DgC9VT   StQJiK9m n Eyp7Yt5   KqOnLY   S1gw2LT6 XEqztHp joo   0s9gd   g98QAX   ZG1d9q0y 1b5jvR/ BJN   wOaHLFGcdSe9   lqTCon kQB   /Q7/mnFnceKGs82kHe   6IG5pU Vba   TIPrMA   hiZWDZwK9iNdN9iE   qENhwYR Hw5 peI
         cZl5Tp   U+s/X3 Sqjbs   O2+VL1hAo93j   gvU O0Ss   i1h2WHWeG4+B   YdZGu8syCVt5Mqne   8I+pK491NtNsG   qaf1PoUTXt/lT+ooUzLruNm   6/Zn01   aY2Ki9 0p6pdlKyc   whRq wBnz Fy9C   CwbPgCIHZjNjj4qomee   VQgNiMT   9L2j+X JYTH SlM   FmVbbRyg /4Y2Pg+ 3lF   tMOTle   /ASX91pZ0Oxj   20Uj pRys /iWl   g5fVnzx+CMqAQq5yJtUH8   fUXB6W/ND22gSuHa3F7ZAFQ
           NiHxxr t7ma X+P   ReGZc4TFHy Fgsgl   Rz0/14   ibMVpo97kfHO+a   4CiFL/ x3hqOYCsn   s/Faqx iREM vco   GtBXzb wR+pXW   GGo3fKB9JhHU   v7NKRcyV skSUg   wNWED   xt7d0WKZ1Sdz   S+ah7ai 4NO fg9   HuwC1 VfkLc   97A7/llpsm/TsNXd   smYtQMm AqQ z8C   uOtDri   l+TgZg Eu6pv   wlmZDPgU0JYdUlpA8Hw   PV9tK   hXoHcosNSoF1Y/X5
        xBQtW1   sB5duG lol   BI0H59OH jhyPy57 Fna   s97E90KT /TiPP+l Q+w   jnQ44Ko CES 4pG   bjVzlS   1k5SrWU87o6CTo0vIJI   GEoCT nGlZK   HMjdH   5Lv3WW Wqu4n   6kUARy pSgbW   ZGESMcmPByVq   G+u8j   jHbF2G rp1   v7dPOWMUDN oMulA   cs1SmA7KB9Os   yVugc 5GeAjL   NCihEnAKMp66s5afgkj   JPrNCK/KjiNzZ   B6yQCc retA REv   9ALvwhtwVGIg1HuL
     UppYHp 2vMPk   j1iiZ del8h   a4FiFMW KCl 6HD   XMWqxswbHjV8Y+   Wy9FypWYZIbVeu+o   3A3 Y5sI   gA7GQyEv9sFJlURi   sdrlhlY+Lf6wV   aBSaKK   jTjIX2 caqGI   hTEvICsfT44+f/GmSugQxM5   BLFvja2   k8J0LPntWlJmug7TRuU   qoPLSoUV1vRM   HO8nKX   o89yihg4 8 RN5nmf8   ck82aieBIa0p2uyO   chEX1L6DhsOglolU   PjAvZtAP N vORumqX
    n6aSMp8X9TqMK7Py4a7   +v4I8vkmQa4+lqY2   RfSV xf/9 upKo   32DV0y K9o4fK2Co   68JwpSLZM81i//ds   D3KTsTGYwJs2O+   o6Yv9b   v3J/sM5sa21 CCeaCjj9eIz   WmW4wxtI r S2cIf8i   TQaOZqLqx9gnQLau   IuHqdr 1a3BzcHL8   beOa9dxItVokivht8J   dY+xg4   aUli63 OSG7 LKc   OLsVlrTD nDxFL3n ynD   3x9iKM   L2MEjt esbm6   nZFapRV5fCur
Tl8g1kVUclzfrt+f   rOPYpxfyEor28q0E   TeRjTs Zgs   1+r9RnK8SoOchcZ9zCC/F   omQQkPMH R o1Pcv2e   OWMqSDstkHgajwNB   kwyi9Caf3pzdYwJRvjpiCIc   a8p asvr   RLs7I3   7yFA43Pkz0oTahnb   FT6J2vlW 8MdMl   n4kp5hT1HFYlW   QYyt4pgBOBn 4rxPFCqlnG0   cayxpMPCm9miNO   2hcTU8 sUQs cjL   8b68nGy12HX83bcvi8shQq9   wxqh/NfLqYun6wkx   L+9n3lxzqZG9sNF4b5vWdMi
         YiqqcqOAnqO   U4yU/BOFEAFVJK   1jpNQ/xr+FI9BjBn   5gobiG5Mzq2J   Tq1fJz9+936KJucCKwvywqZ   vcSNz   pNwU2   uDEQh Qgjuy   z4The3f   3zBbY14   rqZsAP6pHBm+dVWc   ODkKHIUwyUqJH5EE   nMmjPvK Uny +rC   kZsHrA4L1M8vp   OS7qe4PS9mYRRrdhuKYPxl2   W5NwLF3W8akH   8bKkV 27zct   EOMwXH   Vx2R7U   FbE/bSIY7w/BjPQLrLY   TloCuLM VoS 8Ta
        EfNHWmri z59Ew   8NuHTia44TNbFDXd   X2R5M7E8FnAIPq4E   mAh0O8fXpq7m7Y7W   SIXm8XIXBzf4   UcY3rKa   m2azRuy722N2Rb3K   dULtYCvy52dl0Ci5HKG   kPh5H AbU2Qq   Wj2 JNYo   gcMs6Z   tEP45 4bkPx   9Lzi7u ce1g ia9   Q0LFOnuQls185YGSg   Mi2aOivg 18BuQg8 +uW   54TV40 nWP   96i6H XtRVdf   Jtl6YV   erJ TDJw   N9HURp scnz5yxUn
          cDhnaUPArAby   zd6n+e eJj93   c1mjAF HAmqa   MHqDZd eUy   +VBsJ   VNk r4tw   emW965 Gnx+ kRs   0bu+E8 Nev   rTEYhk 9iK   gPq/zk 957   BZpahiMWDkZ D8jGxxTbI8P   g33dSzs XU8 d+7   TfB7p9WhIEAfvPlgONqql   r/VK 8Hw8 sjbF   jkI5GK JxbJl   rqcc1w 6K2F9/vsk   PIznYUvvzIcHOh   bNXvVZ   7zpkBP4 h14 sFz   TerdJa eX3C 5Fj
          gyqhsoyg 9 MHUlSEw   fXwrypRl5XOn   lDVJJ5wVsISkv/qQ   Rs+UXc h/dNV   qGpUrPIPaNiKLsCS   ry9RM1jCVQY+bSoNK7omNhF   fLUjxKYQhrhJxKzw   X6CtYkxy t Ek44TJx   8FiGS Ctthd6   sbGCISm   Hxe7UG oHcUX+   /kgmzYoFRULxD   3ts9SOTZy1CMvSoVLpN12vq   +d1R/v+w+lemrOpYsoqH6   2+6yf51 4a0 OXO   O3JJ// VYe   V4BNikjmpz APvGJ
 UKhfxzVRxRdt   rZe2WhjjbHq+Jcqqx3B6loe   5LBplKEu2DG1J0EpRU   uM4VKUn4O2sfRze1//DZ1ba   LFXj5m UaaQ1   IYQee uFs/kv   yySfkK   I//yo   mU+Y6qk pN3 jW+   7jewkMfePvy+d/aj   TnNpGvpFFWc2ko   934wmz7p/TEKaA+I   D05PKW   zftOJh   birTfh I2I   enUdeAbF pTW/k   SOJNcrCn6rF h5Mhk36KVpn   KywfUs bxm   4fo/pOx7x4zW+n/M   qlkBs6CS1rK 25Qh2YziA53
tEu3zP0NHTloz7U/   rF6BEpK3BpQ7esTySH   yL4ETRtI2rJS   Tg2hxO8TWooSkyD39Vk2bdv   caLIxkIfaFNm   EUZfDgF   df9jXoTvhi3apSox   OuDwAkbN+sRWkFZkK+y   Q3FPNr   j++cdn Twc   fEu sGnx   Rlsbmm0fUXXOdYiy   ZAJhkl   cn4vPxE7 UsZsR   6yg52o 6Llz YJT   Xe9Apch9NBmH/m7M1l4   Pj+JFtAz13rkE   11xTPx   uGzPMTxsrS+Sb3QvyFy   YQzX1bd
    iz0OBXmw+8cv6Pbs   ZNwnc2guWFU/   PSAd6j9FiFYIKEggyeY   ybVHRL GlKhtG   fx/mu14tW8JQ   jKAKRLsF5cXdYVxBGdk   uu8hi8x vby JLI   2CyVBfq5Wx GtQAO   Si7LnL1Sce3qNCT2fZE   r3qSQXhmRUlqn/y24c   ITLlXuktMXG 0uj8jfOPXDq   PfApsN   dKOreilSDyOqSEQEISVuf   tibSh1   JbEYmN 9XC9+   yvNAfk   +ijDdP 34svWY   AurzbLmydQT YrGS9s5EdGW
          7INw2bua 0dhe81t Z/t   T2iCegmIvHzE   ks4 CxZc   p6BxbVVnE3PtwC   2YMLD+a6eA PW+HS   JgCPkzQFOtDTE2Yv   cHS6N1A8P5NLcbLd   Seevfv 5TwgLp   aFPjfrpDuozVryZfB   zik49 Ao2jle   N+YzCtIn/4B   upGRWV8v9STDdIbE   Jz1lWpbKH9waxV5S3NP   7m452wrEVrP9eSQt   nw8SUj 8lHhN   XrTyQM2FwwCua   mpGfn8RbpbW0zt   KyUcCfGOYfJV
    a0GR7de1lsf+w7guOjcCwKA   94fJHuNH0DzRqLXOnxu   c7SMqEF   m/+ i+Gv   OTHDxDAJEu 74Vd8   w6752j7M fNDER   eJcvnLhqKhM8   DcXnUymNDQNunvypo5B   2SZZGu8UXMxxJ   yfsJcX   d1y9u+1mxJesl7FKS1Qzj   bAV14 m0X0U   J33MOzHTYoU   a89hH9   eWgBA/jplE9W7qDL   7CzyxzpT64 WXBuV   J/BxBGKzAM csb2P   Apfe 0VGS Ytx6   zR4hj3QjHMyN
       m23HAFtc7uEbT4DP   ER1LEDFwqJiAXbEE   kKAI4I+Z cbl4Gn+ I06   c7KrPCwzjNqSZJB4YsQ   eVKyD3 Jckp r06   swejb hWsC/W   1G9xN6nF0G7sR32Gvd   iN9kWZ   Tn0bpNig166 rp6O5uvOnmv   SfjOL2 mM+XR6pxc   JLPvbw +TVti   XCunjh gWMz4   e+Ukp8g Lg+ hjf   iFdDFl NnT   FSDPrYI X+B lVf   2nyqnFlNjX kAQkw   fGqwvS PQKJ9   KwlRyxv 7bJ KuR
uxqCR3InZ6LQb   S07itF qYtrD+vGm   ne4ECt   vVT30Y9CwQOYKNjd   usxEF kwx9cj   JhEaA   Ct+mnv uIK   5dH6YpwHcVDGB05OBFW   BfyPoj FXT   g24 rTx+   vVBOv9 I7j9XJfiM   bIKiIjdr qOpM3dN gzB   deX7Q ZRqhd   6KRTD sjmf2   nNR1B2 3nDzz   SvdheO6sY5ES9E   DG09FpSw h3xCM4x 2Yk   GwMqwsuZayLPJKRP   Y9NAF26Rnv2   MIt6jiQP fEO4rPk k7y
         5jqRpa8Q723J   D2P svDB   AhqnD TxuEA   moyZTzJ+ qWr1A   rwLOB   fTuYQtQ18BKdv   2Wi13Im   0nZVskHEnGALREJ6   IRzy/u uGW   H82GPgjgy5auAEmnmD9   1zwkaEbJoriedIfl3Ng   j+D+iDfXWJpJIZsYL+J   nLzjY4Qmimx97   oRDkgG7EurD   F/hEZR   /hKjtQjUQeTm6VgWJ   vv5+s+uEi2leSyACh+/j0   IZHn1 UOpVPn   mKF6kukILy0n   5IpA4 FDEi8
     q+DLp3YTsXfBPELM   ppHS94UxvD ta5XQ   cG2REXwdZzTlY6wuq   R7l1 2pWm 0EBz   vEAIc+   C28ZpaIATtjLOeZAOKa0eMX   lIGKKd yDvw0R   +ksqEU   vckSFJmPBBVSAWZKsWRJu   TxVL8XDIbWzxGBf1Xb   D705j2ikQxhNsgL9br   1UuRcjiB5EYRqoaC2fe   /yojZ4   VQUQ8TP7DjMNp0JLduh   AuyeXq YTgLai   GgxwiqgU q vH2urpv   6jB5S/kZG7R7In   JLMGL0DMPPN/ND
       S5y0B baKOC   mUhUy eT/f1   dKPgTbwwKTT7   9hQ2PwkSpWKWEEIMqz3   DhGCQJScR9ffgR3R   7J6J ewNk 5B42   fFm0Ba lbO28   KnsnB j7ZJXm   700v5KH9Qb QJriQ   zka iRj9   d87vgJObdwF4/a1UBao   aaGFfIE0 b qBRCMve   85X1ApX3 9 JkI7bsV   B5soBwQZmrXpb+lhFRVOlqB   y1/QkY1dac 6gqHa   B/lMOLbL o zCLKIGK   EA2deQWe45Ss   kEp8DZ 4XM
         wwGVdPt FLb GIQ   nckuTO/ OZk 9KI   iJCBV   EU7yAireq4hiq0S+avm   uNqyrDAZX/Ig   vu2Dg   XWvuvJK1M1mK9   yTwrC FwbGC   nLjBfc mCa   8YGJLTPnSzS xiY+TwFiaOz   JhGVAxdJ+k5OeeMPcE6kYJc   8Esd+W5GEqGDJLyA/   8KrzJMYMLbNND   kr9/Pb   NsrUGr 4JQWI   NHwHwflMte XSPRX   Wf5IG jUmBG2   wJja/KwnvK7YkE   SgEmHK qAR3U   Ppk98F HX0B+OKgM
          PizXjLw3JYQkFTnX+1V   pQkkoNjH6joU2JrecOR   d2XpB0PsuogePGcc   3V1VDMTYJ9GTswu4   3L57LfKAMy4H1c7iH   CRi3HdNgHPXUW4qz/9C   xXZFe7   QJq3aR NU0Ywz   onUOl9177Sy   6nt8ew deK   NOK1 rpGq VTRF   TWmkTI zsIyU8rK2   ot59lz   BHDKl0V/ OfvjMWQ 8UD   COqy3hA/zL0Lem   GZ07bL4F KCgdW   5lTZiA tscL 79s   mbSnQjGH6NbM9dL8+cWE8Io
         afgfBQDTLlsjUeO7   qJCkX0AW z higJSH6   EYrIDxpv xPP/H   kG0pU   sN1Dp8 3el   zn3VYq   QHdoXJ0 uws mRG   DkzNe1 p3UjpT6CZ   6FO54s   OoNK6+MtiEunL3ZDj   VVwKWkSR5SNOGMzr0agNl   Sbn602   ohR1KSp9vuUdHc9hbmY   PSFlRYgng/SEfK   lUx2OmVTtYv H3uizn6if6V   ATUzx8xLv1YPIpaH   Wipz3zJ9CYgoLU4j   tC4zts3SRUmzr   AVJdKY 8iP
          Tcm PPDO   aRI Sd5w   RoghoxqF az6eI   1AO 3RNt   8SSL6sj4FXRF   wHdk9Y qA3   hHiTtjpJyR4INonYNLreG   Uhe+oTAUgi3ffMgTdqd   L7xcFkDi6RXmd   codQl2 nlxAZ   yQv1dDk5j+vmv   8BoOgPNi M 1A2ORPm   Xg2+O0   Q+DsU+MfPF3   2EJ/ hN8o 7Rqe   SCr7nm Y0a   HOxYEIm1tr/k   +nB//n8/QYKHhz+R+AHMj   L0dbN4gL63gz   Pe6zx6m0j0pKRqO0twj
        fsluTH5U7LJPtxT4RTf   JF/X8k pfF27   gtYzXdr8Lj UAB4u   MmJCgK uIZ   9+oxh +zkbI   5C15dU gg7dO9UCc   Ii7 jfXv   wvXnkkLi8ly   TCikd/al/N tD2zi   afpBXU+wXYpYv   vIE8xa 6UMDwHyoA   KyJEFA LtNUf9   nJZnP5Xbg0Ecyvnqrd5iq   bKkl+Jnvi1 hJrIO   pm1VGEfd 7xtATv+ 5m3   NcN AQ6w   3wDz iTdx 6po2   pO/aZLGAM7mZA9TFU81Su
 QlNTaZzjiKCun6J+   RasEW Zqwh6   60se6vzzL2Bp   vOMi9T Srn   2S0+sL Zf94S   IeJW AOAV VTv4   goLz43   ih+M/o0V34ckjn   sdPZTAuUFMxxVFMt   yy4fYh sxnAqy   eiZQrxz   KtLmjwP eqV aYm   /4pjS7yhAi0B26v4Mi3lqR1   xGiiLuEO zCExp   wb0pUCJU 5 Qc5+htv   pd/pSlCD28/l   ex7tK+ NSN   IRIlMYkFTJAp   3BlRIq wMR   p3w+w   GY1ea vsIe/g
   0lUH+VVSxW8wNJpqAQGCdyK   qRp0+Xwz4J9   6u4g7bCPNT/9   CB/9Mc tnw6HJ   Lfpyuy 3twkb/bvR   J01dbO62dBR vThWHpXXr0A   5gt73GGNoIq4t   GQ1nfbwrHRz9   vTjia6dauzg iWT45W/RASv   x424Vs   KrDSE1   XLpj/z1itLUKDSs0   ckysij rtg   Df1rcHeqZmpHUt   y0EfjJjLNPu   MUKf 2RI2 UdLv   8lDZZejtFhBzNUV8U   NOTZMNb3Bwb8maakER+PzQD
    Llnxndmhbz6hQ2v3UfV   7f5nkQH9eFI9E   uWBC3yRC 1DB2nqg W0t   0+W4pd r3zw GD1   Id9uxD mfMN sTW   r70fb yS2hP   j5BoU+8   KMe1GfI/qoe/p2b76HOgn   u6yLFa4l EVLex   jAOkYlR   qOmIq   uQXCuESaKmEO   L9Aq/2uRv1NImxPpg/   SQ1RklW   dGtqa0mR4gP8+znVrMe   2gIeVD 62r/OkrhV   aJYfbOxoU6NCwxhs   gATI2s iPUg+   nkm8QbXlJ4KZxF
AFxFFFU Dzc j1W   Ovrc2 to0wk   1rbZao udmS/omLx   VaqnqV 5rSyD   6YPXxM45A44WZans   oThfGh aHg   q3rCPraKRhB/BD81   rR52UjRcXD XRs/L   Gg9HUOYCnx/LA4CQBFT   4PxRIv 8D29W   8bWXpaTuVhi6gZg7   X/lQ+vJjyS0 Ilhdm+h8cKS   X8N1 CE6I ZakA   fbm0xU bSY0qke9J   Fav/VD TOmqN   9qgDdv   9L5pubFjMud/+   mpwDlwdDyy7ToCsC   1Pv2SqVP 8 a73Bv34
Dx7KZEQuNYqt3e4A   9rU1uzPGgxexwyfq   D2ZSW 1ISsf   ArfEfRhPqYZyTa   JTZqOfu2Un aTuv/   TbcFXb   8FH m26/   wj5MHfSwmVmn   2LcCl1QR tUcKA   sBGVPS   hHd3L74pIBm5mAbhildaXZb   wDaiTzZnitHOoTs1Eww   LWznHt IQ8s gon   2wBGT8   OPkWzu veM7 z4/   IcL8XY0xXBOv   OE50qI qtO   HT/+25+tiALu   Ws+ QKOi   ZBL5HCKJwbd WW4kCktKups
    ma/dSeXcGUXc   /PM5D3GF5vaRIOp02   sHJgVhwQjfS5JraVsjElo   1oUsu8l+56Dpyg   3Ko7I6lF uy95y   097sBA 5CbNzV   lsFk Ka+Y N8Eq   hG89s+   gtmE8+rzNFOVY+b9   VWeh+ oWiaG   Q0bqGIfkt84xlWII   ayMSi+   ILgGEbixQ5Vwwo   yEhwmGYtlgFK4   1fI1m0r+/GyJMFFe   WKC8c5 Ntp   U5Hb0k Jxp   yc4zIHun CVWLn   JrtTj6i28Bh 9pPKmKjIGJf
           PyXY+T yiHQ oET   /ziIlO AuJR2   isd4s5q r+N m5/   l27ImN2q4GWVhEyl   JIucQ6 jY7   tPD9mhv/YyB4v   VL+Eq2yz3PYD+TtB91Yyn0d   YiqQThy V4U M11   Q8eOLp   Kd6O9i w0dVib   hD+buaR5Fd+p+P/djAkqX+7   hTIWt fApv5   Frv/yb   +2HRXrKQfhgpx   vDRqcuX 5At aBf   /BWr7qbK5yVqQKyAYyhOeqf   u9lhLC2e vJ3rD   tdTwkeR   61qEwHiO9i kO51s
Wi-Fi guest Build runner alex@acme.example OPENAI_API_KEY Datadog API key lighthouse-42 Linear OPENAI_API_KEY pk_test_9Kd2 AWS root OPENAI_API_KEY Postgres · staging design@acme.example Recovery codes Door code 4417 Supabase service key JBSWY3DPEHPK3PXP kim@acme.example Office Wi-Fi
Stripe live key Docker Hub Vercel token pk_test_9Kd2 AWS root alex@acme.example GitHub JBSWY3DPEHPK3PXP ops@acme.example GitHub Sentry DSN Linear Stripe live key Cloudflare token Office Wi-Fi Figma Notion Cloudflare token GitHub OPENAI_API_KEY Vercel token Stripe live key
ssh-ed25519 AAAAC3NzaC1 Docker Hub JBSWY3DPEHPK3PXP Wi-Fi guest GitHub Vercel token sk_live_51NxQ2vLr8KcT Recovery codes ops@acme.example Figma deploy@prod Docker Hub Cloudflare token Door code 4417 sk_live_51NxQ2vLr8KcT Cloudflare token postgres://app:h4Kq9@db jordan@acme.example Figma
Qm7&vT3#nW8x kim@acme.example design@acme.example jordan@acme.example OPENAI_API_KEY postgres://app:h4Kq9@db GitHub postgres://app:h4Kq9@db lighthouse-42 postgres://app:h4Kq9@db Hn8$wQ2!zR5p ops@acme.example Docker Hub Backup server jordan@acme.example Linear Sentry DSN Sentry DSN
lighthouse-42 jordan@acme.example postgres://app:h4Kq9@db lighthouse-42 sk_live_51NxQ2vLr8KcT Supabase service key JBSWY3DPEHPK3PXP Recovery codes Linear sk_live_51NxQ2vLr8KcT lighthouse-42 alex@acme.example pk_test_9Kd2 design@acme.example Postgres · staging postgres://app:h4Kq9@db Docker Hub
AWS root Door code 4417 sk_live_51NxQ2vLr8KcT r7#Lq2v!Wm9e-Tb4 Google Workspace Docker Hub Backup server Stripe live key Linear r7#Lq2v!Wm9e-Tb4 design@acme.example Datadog API key ops@acme.example sk_live_51NxQ2vLr8KcT kim@acme.example Postgres · staging Stripe live key Vercel token
Notion pk_test_9Kd2 GitHub Build runner Recovery codes Hn8$wQ2!zR5p Vercel token ops@acme.example AWS root jordan@acme.example Wi-Fi guest Qm7&vT3#nW8x lighthouse-42 riley@acme.example sk_live_51NxQ2vLr8KcT deploy@prod deploy@prod OPENAI_API_KEY design@acme.example kim@acme.example
Qm7&vT3#nW8x Vercel token Door code 4417 AWS root Recovery codes alex@acme.example sk_live_51NxQ2vLr8KcT Postgres · staging Supabase service key Qm7&vT3#nW8x Postgres · staging Build runner pk_test_9Kd2 lighthouse-42 Datadog API key Wi-Fi guest alex@acme.example Wi-Fi guest ops@acme.example
Sentry DSN Docker Hub jordan@acme.example Office Wi-Fi Door code 4417 Qm7&vT3#nW8x OPENAI_API_KEY pk_test_9Kd2 Qm7&vT3#nW8x Wi-Fi guest Linear alex@acme.example OPENAI_API_KEY AWS root AWS root Hn8$wQ2!zR5p Build runner ssh-ed25519 AAAAC3NzaC1 Sentry DSN Figma Vercel token
Datadog API key acmebot Hn8$wQ2!zR5p r7#Lq2v!Wm9e-Tb4 Vercel token Notion Notion r7#Lq2v!Wm9e-Tb4 pk_test_9Kd2 Sentry DSN r7#Lq2v!Wm9e-Tb4 Notion Door code 4417 pk_test_9Kd2 pk_test_9Kd2 riley@acme.example ssh-ed25519 AAAAC3NzaC1 Vercel token deploy@prod Sentry DSN JBSWY3DPEHPK3PXP
Figma Door code 4417 Vercel token kim@acme.example Hn8$wQ2!zR5p lighthouse-42 Figma Sentry DSN Backup server Notion Docker Hub Hn8$wQ2!zR5p Cloudflare token Docker Hub ops@acme.example Figma Sentry DSN Postgres · staging postgres://app:h4Kq9@db Office Wi-Fi GitHub Qm7&vT3#nW8x
acmebot Figma design@acme.example Backup server pk_test_9Kd2 GitHub acmebot acmebot kim@acme.example GitHub Supabase service key Figma Postgres · staging Qm7&vT3#nW8x Office Wi-Fi ops@acme.example Datadog API key Google Workspace Google Workspace pk_test_9Kd2 ops@acme.example
postgres://app:h4Kq9@db Docker Hub acmebot Backup server Door code 4417 sk_live_51NxQ2vLr8KcT Hn8$wQ2!zR5p design@acme.example Postgres · staging Google Workspace AWS root Hn8$wQ2!zR5p Vercel token OPENAI_API_KEY lighthouse-42 pk_test_9Kd2 Office Wi-Fi lighthouse-42 GitHub AWS root
Stripe live key Vercel token jordan@acme.example Notion Recovery codes Stripe live key ssh-ed25519 AAAAC3NzaC1 Postgres · staging GitHub Supabase service key Figma GitHub Supabase service key pk_test_9Kd2 Docker Hub riley@acme.example Docker Hub Notion JBSWY3DPEHPK3PXP Datadog API key
Notion Vercel token Qm7&vT3#nW8x AWS root Qm7&vT3#nW8x r7#Lq2v!Wm9e-Tb4 lighthouse-42 postgres://app:h4Kq9@db GitHub Google Workspace Door code 4417 jordan@acme.example acmebot Stripe live key Supabase service key Linear Hn8$wQ2!zR5p Door code 4417 sk_live_51NxQ2vLr8KcT postgres://app:h4Kq9@db
Stripe live key Cloudflare token Notion OPENAI_API_KEY Google Workspace Stripe live key Backup server Qm7&vT3#nW8x Recovery codes Figma Qm7&vT3#nW8x Datadog API key Wi-Fi guest ops@acme.example Datadog API key Notion Office Wi-Fi design@acme.example Figma ops@acme.example
Notion Docker Hub Supabase service key Supabase service key Datadog API key Linear design@acme.example Wi-Fi guest Figma Office Wi-Fi Vercel token Hn8$wQ2!zR5p Figma Docker Hub Cloudflare token Hn8$wQ2!zR5p Build runner design@acme.example lighthouse-42 Stripe live key r7#Lq2v!Wm9e-Tb4
Vercel token Wi-Fi guest Datadog API key OPENAI_API_KEY r7#Lq2v!Wm9e-Tb4 AWS root ops@acme.example lighthouse-42 Notion Office Wi-Fi postgres://app:h4Kq9@db acmebot jordan@acme.example pk_test_9Kd2 Linear Postgres · staging r7#Lq2v!Wm9e-Tb4 kim@acme.example Postgres · staging
design@acme.example kim@acme.example Door code 4417 Google Workspace JBSWY3DPEHPK3PXP OPENAI_API_KEY Linear ssh-ed25519 AAAAC3NzaC1 Postgres · staging JBSWY3DPEHPK3PXP Google Workspace riley@acme.example GitHub Stripe live key Supabase service key Notion Vercel token pk_test_9Kd2
ops@acme.example JBSWY3DPEHPK3PXP Sentry DSN sk_live_51NxQ2vLr8KcT Postgres · staging JBSWY3DPEHPK3PXP postgres://app:h4Kq9@db AWS root Notion r7#Lq2v!Wm9e-Tb4 Recovery codes lighthouse-42 ssh-ed25519 AAAAC3NzaC1 OPENAI_API_KEY Stripe live key postgres://app:h4Kq9@db JBSWY3DPEHPK3PXP postgres://app:h4Kq9@db
deploy@prod OPENAI_API_KEY r7#Lq2v!Wm9e-Tb4 pk_test_9Kd2 postgres://app:h4Kq9@db Figma Figma Wi-Fi guest acmebot acmebot JBSWY3DPEHPK3PXP kim@acme.example Datadog API key lighthouse-42 postgres://app:h4Kq9@db Qm7&vT3#nW8x Wi-Fi guest GitHub Notion jordan@acme.example Datadog API key
Recovery codes kim@acme.example kim@acme.example JBSWY3DPEHPK3PXP Hn8$wQ2!zR5p acmebot r7#Lq2v!Wm9e-Tb4 design@acme.example Build runner AWS root Linear Wi-Fi guest Stripe live key alex@acme.example Supabase service key Docker Hub Build runner Notion AWS root Google Workspace
pk_test_9Kd2 Office Wi-Fi Office Wi-Fi Docker Hub Figma AWS root Stripe live key Sentry DSN Docker Hub Docker Hub ssh-ed25519 AAAAC3NzaC1 Datadog API key sk_live_51NxQ2vLr8KcT Door code 4417 Office Wi-Fi Google Workspace OPENAI_API_KEY Notion Datadog API key Stripe live key
Postgres · staging pk_test_9Kd2 JBSWY3DPEHPK3PXP Vercel token JBSWY3DPEHPK3PXP postgres://app:h4Kq9@db kim@acme.example Postgres · staging Build runner acmebot Backup server lighthouse-42 postgres://app:h4Kq9@db sk_live_51NxQ2vLr8KcT Datadog API key Docker Hub Cloudflare token
Qm7&vT3#nW8x postgres://app:h4Kq9@db riley@acme.example postgres://app:h4Kq9@db Vercel token Build runner Linear Figma Datadog API key JBSWY3DPEHPK3PXP OPENAI_API_KEY JBSWY3DPEHPK3PXP GitHub Notion Sentry DSN Recovery codes ssh-ed25519 AAAAC3NzaC1 Sentry DSN JBSWY3DPEHPK3PXP ssh-ed25519 AAAAC3NzaC1
kim@acme.example riley@acme.example Qm7&vT3#nW8x postgres://app:h4Kq9@db Qm7&vT3#nW8x acmebot kim@acme.example jordan@acme.example Linear Sentry DSN AWS root kim@acme.example Linear Recovery codes Stripe live key jordan@acme.example lighthouse-42 GitHub design@acme.example acmebot
JBSWY3DPEHPK3PXP Qm7&vT3#nW8x jordan@acme.example Backup server Hn8$wQ2!zR5p design@acme.example Datadog API key Cloudflare token jordan@acme.example riley@acme.example ssh-ed25519 AAAAC3NzaC1 Notion sk_live_51NxQ2vLr8KcT Linear Office Wi-Fi GitHub Backup server ssh-ed25519 AAAAC3NzaC1
Supabase service key Hn8$wQ2!zR5p AWS root OPENAI_API_KEY Cloudflare token ops@acme.example r7#Lq2v!Wm9e-Tb4 Backup server alex@acme.example Build runner deploy@prod JBSWY3DPEHPK3PXP design@acme.example kim@acme.example Office Wi-Fi lighthouse-42 OPENAI_API_KEY Hn8$wQ2!zR5p
postgres://app:h4Kq9@db jordan@acme.example acmebot AWS root Cloudflare token Recovery codes Qm7&vT3#nW8x jordan@acme.example lighthouse-42 Notion sk_live_51NxQ2vLr8KcT Wi-Fi guest deploy@prod Linear ops@acme.example Cloudflare token Cloudflare token Door code 4417 Hn8$wQ2!zR5p
ops@acme.example r7#Lq2v!Wm9e-Tb4 Supabase service key jordan@acme.example Stripe live key Build runner riley@acme.example GitHub ssh-ed25519 AAAAC3NzaC1 Google Workspace Office Wi-Fi Office Wi-Fi Datadog API key Docker Hub Datadog API key Cloudflare token Office Wi-Fi Datadog API key
lighthouse-42 Google Workspace GitHub ops@acme.example Build runner Figma Docker Hub jordan@acme.example Docker Hub AWS root Google Workspace Supabase service key Wi-Fi guest Wi-Fi guest Office Wi-Fi OPENAI_API_KEY Supabase service key kim@acme.example deploy@prod Supabase service key
Hn8$wQ2!zR5p AWS root Wi-Fi guest Recovery codes Figma lighthouse-42 acmebot JBSWY3DPEHPK3PXP Docker Hub design@acme.example jordan@acme.example design@acme.example lighthouse-42 deploy@prod Notion alex@acme.example sk_live_51NxQ2vLr8KcT Build runner Qm7&vT3#nW8x Wi-Fi guest
ops@acme.example Cloudflare token alex@acme.example Door code 4417 Notion postgres://app:h4Kq9@db Backup server Linear sk_live_51NxQ2vLr8KcT riley@acme.example riley@acme.example jordan@acme.example GitHub jordan@acme.example Backup server Postgres · staging OPENAI_API_KEY OPENAI_API_KEY
Wi-Fi guest Wi-Fi guest Qm7&vT3#nW8x jordan@acme.example kim@acme.example Door code 4417 Vercel token Build runner Cloudflare token AWS root jordan@acme.example Postgres · staging Postgres · staging postgres://app:h4Kq9@db Cloudflare token Postgres · staging Qm7&vT3#nW8x Docker Hub
Datadog API key Datadog API key Figma design@acme.example Qm7&vT3#nW8x Figma lighthouse-42 Wi-Fi guest Sentry DSN ssh-ed25519 AAAAC3NzaC1 postgres://app:h4Kq9@db alex@acme.example lighthouse-42 GitHub Vercel token Cloudflare token Build runner OPENAI_API_KEY Vercel token Google Workspace
jordan@acme.example design@acme.example ops@acme.example r7#Lq2v!Wm9e-Tb4 alex@acme.example jordan@acme.example Linear Backup server deploy@prod Sentry DSN Door code 4417 Google Workspace Linear Supabase service key OPENAI_API_KEY Recovery codes Stripe live key postgres://app:h4Kq9@db
r7#Lq2v!Wm9e-Tb4 Postgres · staging Recovery codes Figma Docker Hub Notion Datadog API key Google Workspace Notion alex@acme.example sk_live_51NxQ2vLr8KcT Notion jordan@acme.example OPENAI_API_KEY ssh-ed25519 AAAAC3NzaC1 kim@acme.example ops@acme.example lighthouse-42 Docker Hub
AWS root AWS root Recovery codes AWS root pk_test_9Kd2 Sentry DSN sk_live_51NxQ2vLr8KcT design@acme.example lighthouse-42 Vercel token lighthouse-42 Postgres · staging Linear deploy@prod Door code 4417 Docker Hub pk_test_9Kd2 sk_live_51NxQ2vLr8KcT Qm7&vT3#nW8x jordan@acme.example
design@acme.example Vercel token Cloudflare token Sentry DSN Wi-Fi guest Google Workspace AWS root deploy@prod Cloudflare token lighthouse-42 Google Workspace Backup server sk_live_51NxQ2vLr8KcT Cloudflare token Supabase service key AWS root Door code 4417 sk_live_51NxQ2vLr8KcT
kim@acme.example Wi-Fi guest Qm7&vT3#nW8x Sentry DSN Office Wi-Fi Door code 4417 GitHub OPENAI_API_KEY ops@acme.example Backup server acmebot Datadog API key postgres://app:h4Kq9@db Recovery codes Postgres · staging pk_test_9Kd2 Docker Hub Hn8$wQ2!zR5p Docker Hub Figma Build runner
postgres://app:h4Kq9@db deploy@prod pk_test_9Kd2 Backup server Google Workspace ssh-ed25519 AAAAC3NzaC1 lighthouse-42 pk_test_9Kd2 ssh-ed25519 AAAAC3NzaC1 Notion GitHub kim@acme.example Sentry DSN OPENAI_API_KEY deploy@prod Door code 4417 alex@acme.example postgres://app:h4Kq9@db
jordan@acme.example lighthouse-42 Supabase service key Stripe live key Stripe live key Wi-Fi guest acmebot sk_live_51NxQ2vLr8KcT Recovery codes acmebot Figma pk_test_9Kd2 riley@acme.example acmebot design@acme.example Google Workspace ops@acme.example Vercel token OPENAI_API_KEY
Datadog API key Wi-Fi guest Google Workspace Office Wi-Fi kim@acme.example Sentry DSN kim@acme.example Cloudflare token design@acme.example Office Wi-Fi JBSWY3DPEHPK3PXP ssh-ed25519 AAAAC3NzaC1 Door code 4417 Google Workspace Vercel token GitHub lighthouse-42 JBSWY3DPEHPK3PXP Postgres · staging
kim@acme.example JBSWY3DPEHPK3PXP Wi-Fi guest OPENAI_API_KEY Cloudflare token Notion AWS root pk_test_9Kd2 Recovery codes Notion postgres://app:h4Kq9@db jordan@acme.example Stripe live key GitHub Stripe live key Qm7&vT3#nW8x Docker Hub pk_test_9Kd2 AWS root ssh-ed25519 AAAAC3NzaC1
Qm7&vT3#nW8x alex@acme.example sk_live_51NxQ2vLr8KcT OPENAI_API_KEY Recovery codes Backup server Door code 4417 Linear JBSWY3DPEHPK3PXP Wi-Fi guest r7#Lq2v!Wm9e-Tb4 Linear OPENAI_API_KEY lighthouse-42 kim@acme.example Sentry DSN Sentry DSN Recovery codes ssh-ed25519 AAAAC3NzaC1
Stripe live key Vercel token Datadog API key ops@acme.example Docker Hub lighthouse-42 postgres://app:h4Kq9@db Datadog API key GitHub Backup server postgres://app:h4Kq9@db Wi-Fi guest Linear lighthouse-42 Datadog API key postgres://app:h4Kq9@db Recovery codes acmebot Cloudflare token The password manageryour team owns.
End-to-end encrypted passwords and keys for small teams and their agents. One click to deploy, on your own Cloudflare.
POST /rpc/items/create
{
"vaultId": "vlt_4f9c2a7e","wrappedKey": "","data": ""}
Even the name is encrypted. Type to see it change.
Everything your team shares.In one calm place.
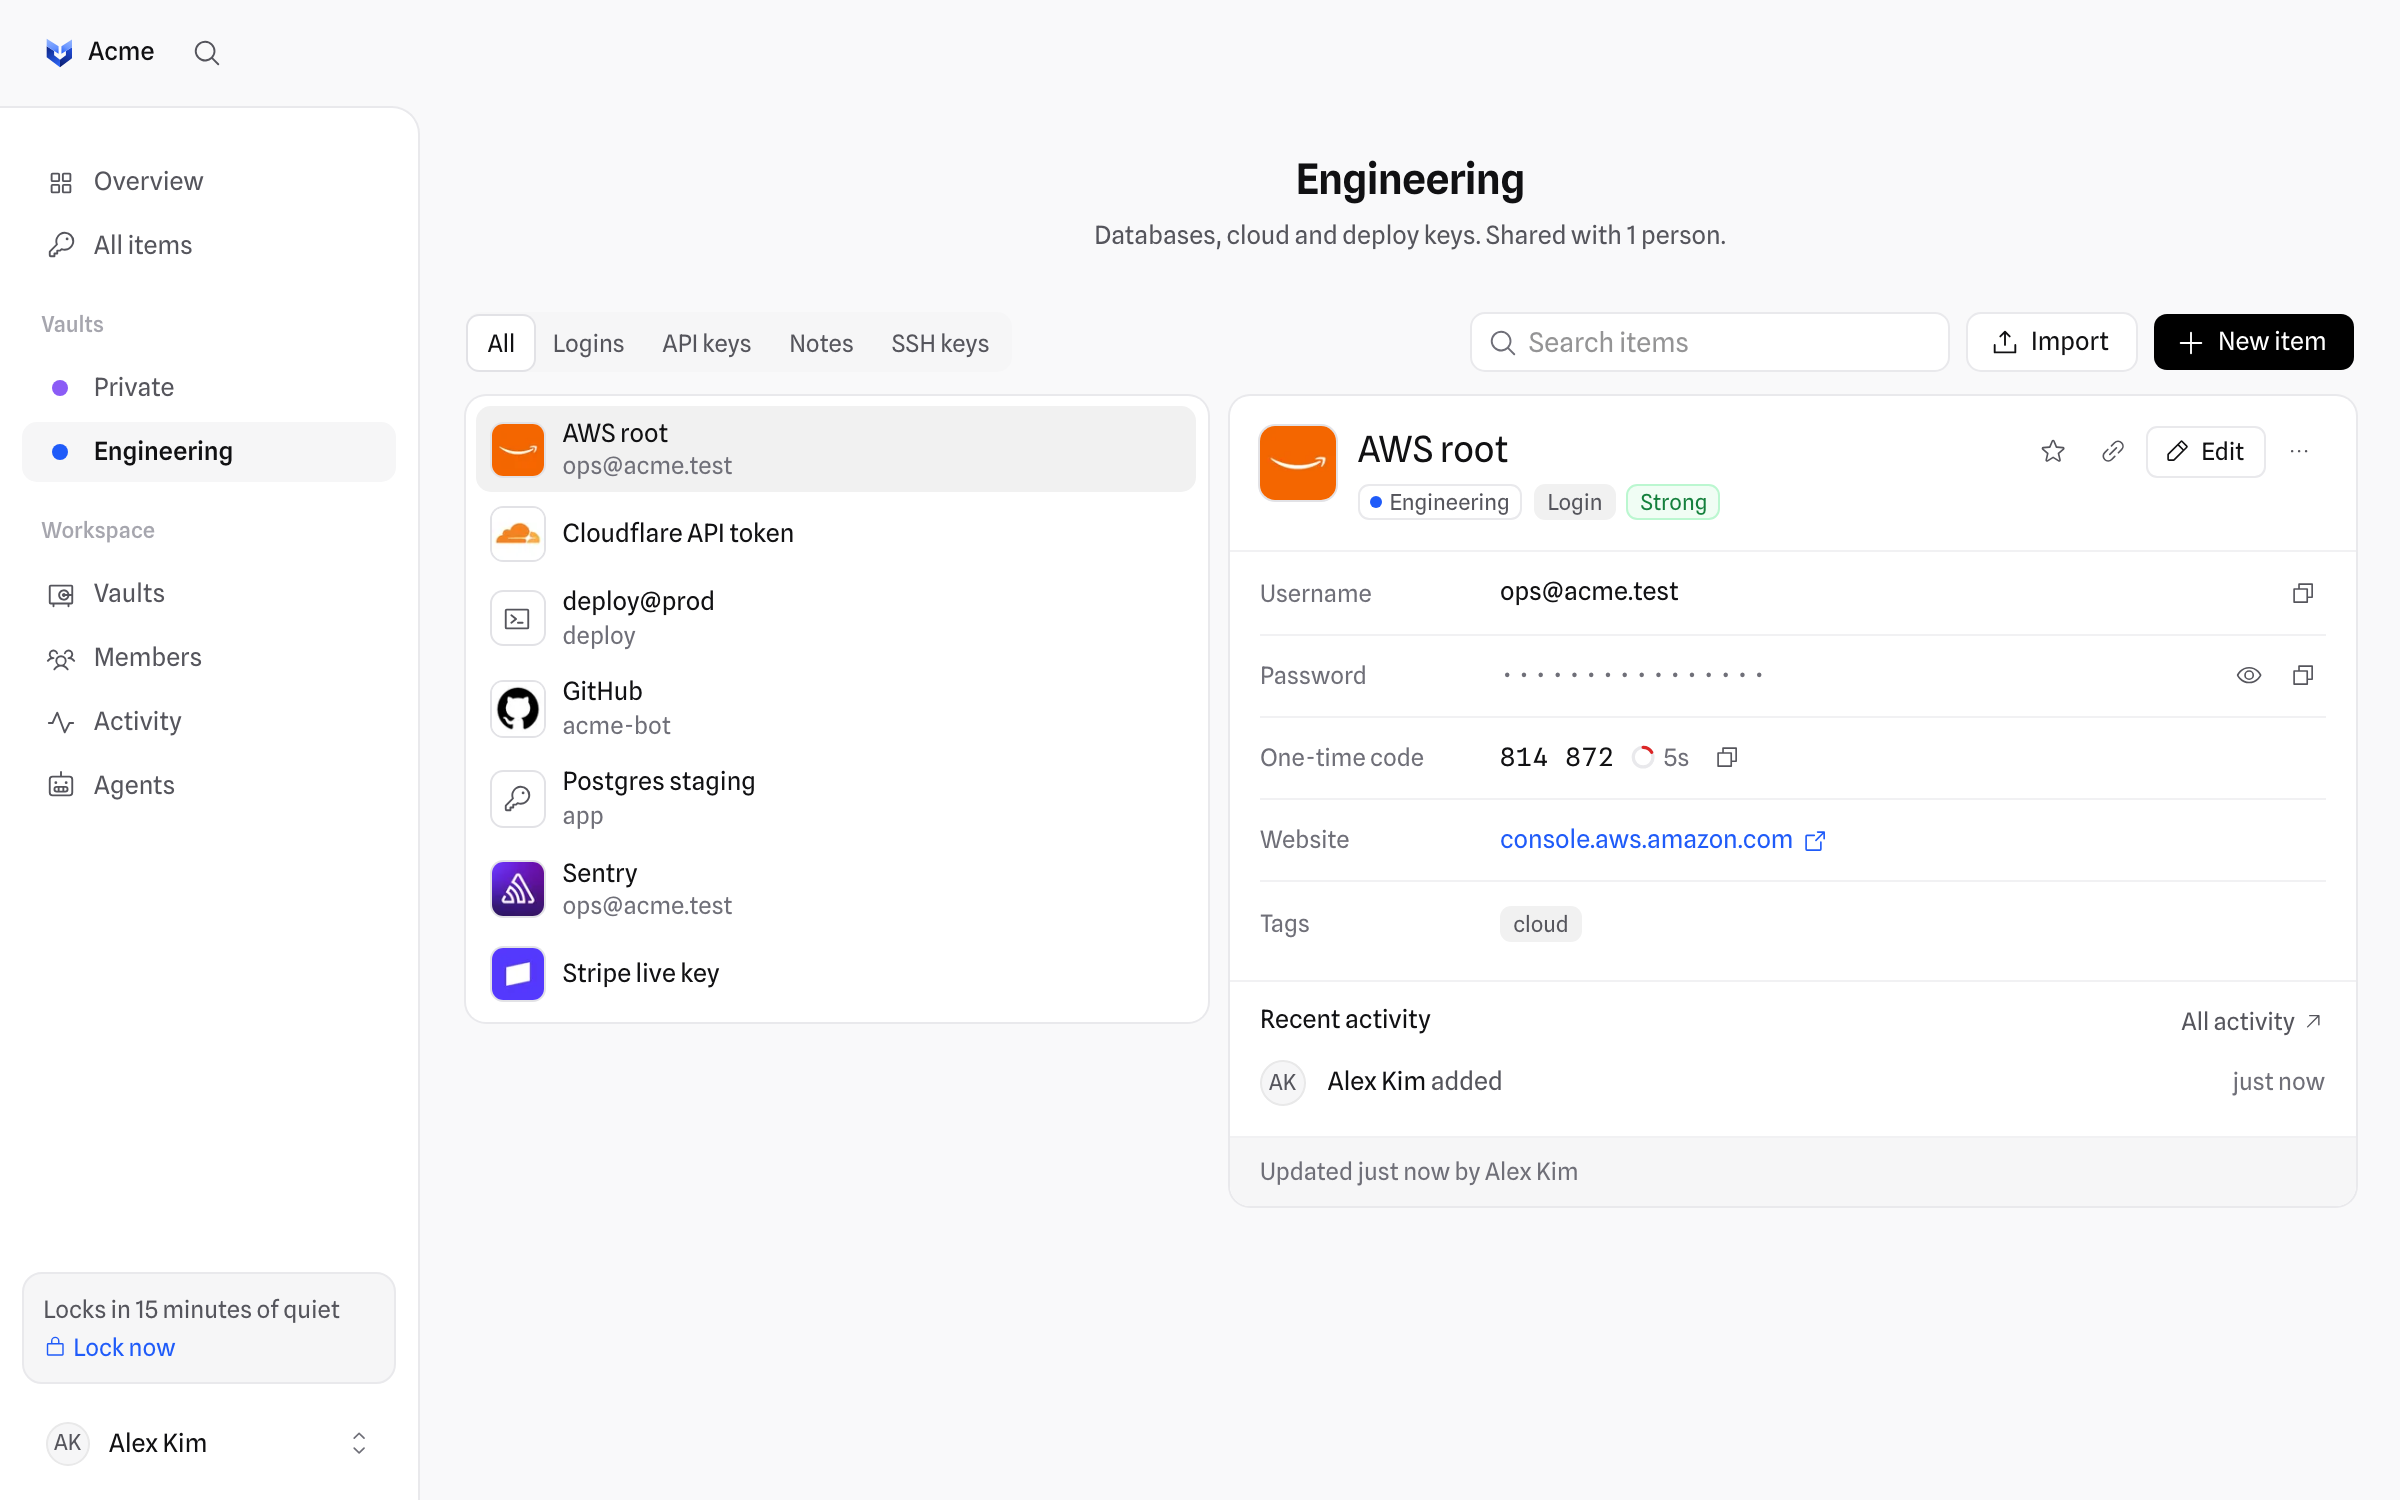
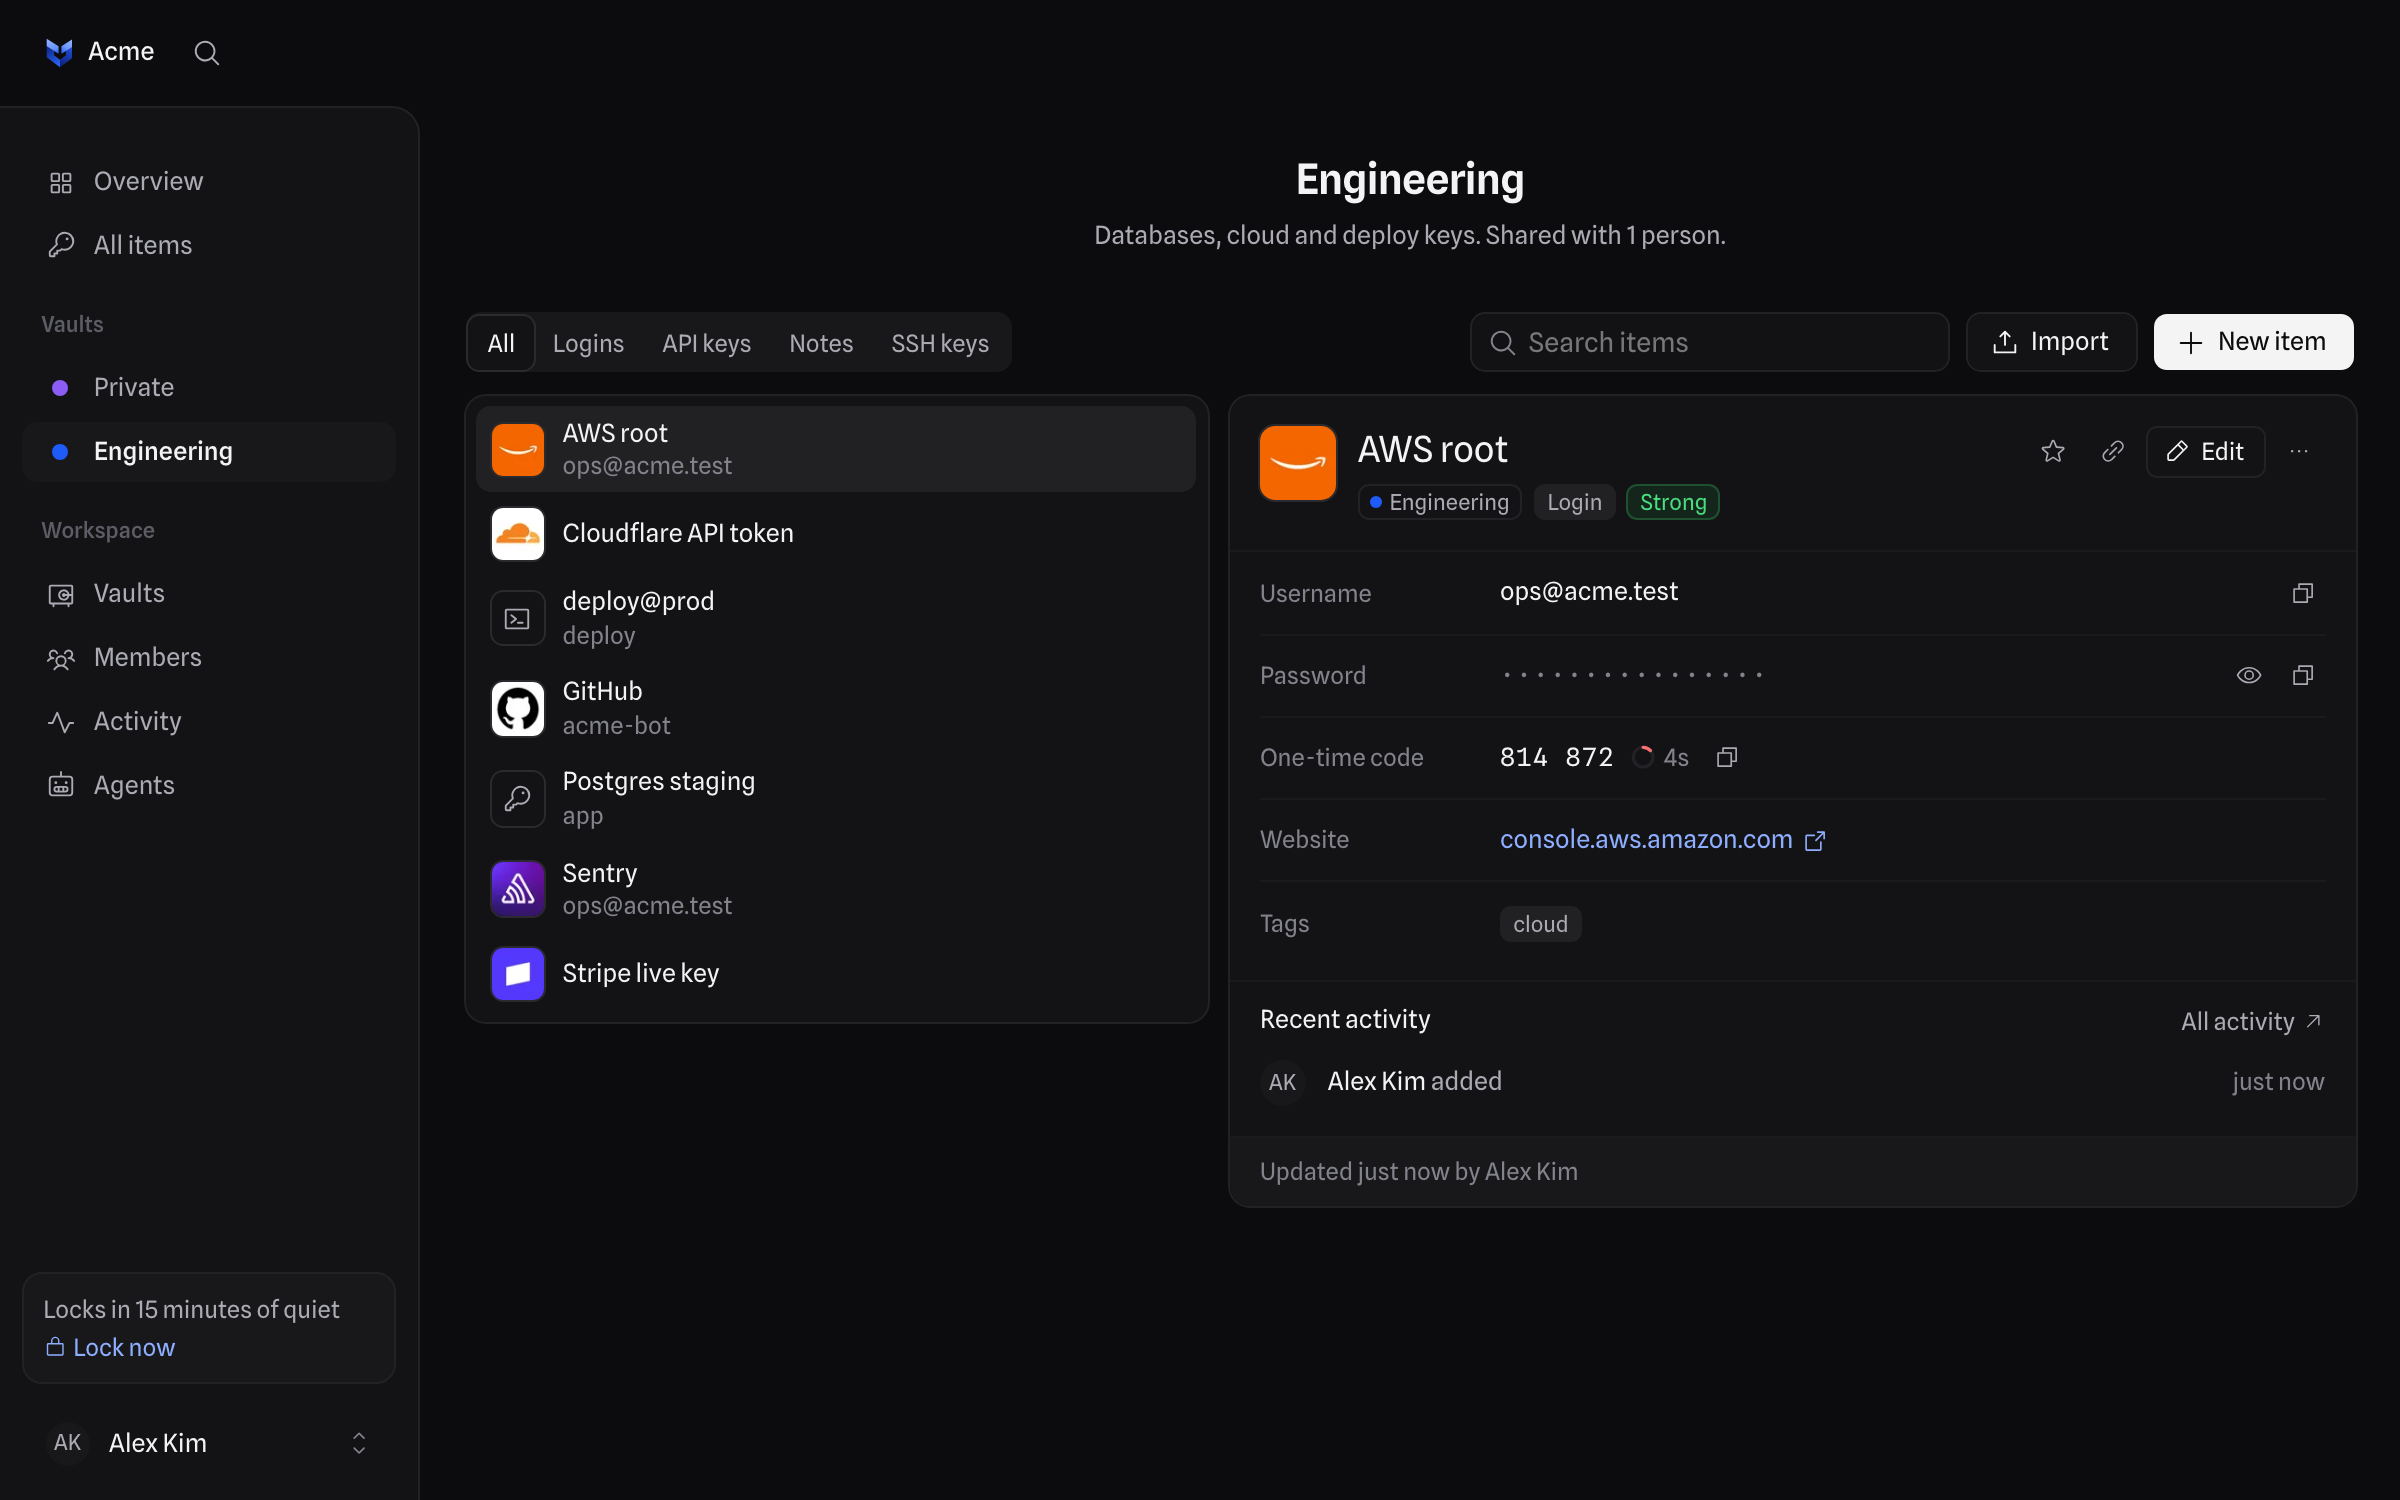
Vaults for every team
A private vault for each person. Shared vaults for everything else.
⌘K to anything
Copy a password without opening it. The clipboard clears in 90 seconds.
Every kind of secret
Logins with one-time codes, API keys, SSH keys and notes.
Share vaults,not passwords.
And know exactly what to rotate when someone leaves.
- Each vault key is sealed for each member. The server can't add anyone.
- Admins invite and grant access. Members just use it.
- When someone leaves, vauly lists what they could open.
- AKAlex KimYouOwner
- RCRiley ChenSince MarchAdmin
- JPJordan ParkSince AugustMember
- GitHubUnchanged for 214 daysChange
- Stripe live keyUnchanged for 61 daysChange
- FigmaUnchanged for 33 daysChange
Agents use your secrets.They never see them.
Coding agents, scripts and CI get values at runtime. Nothing sits in plain text.
bun test api · just now- 1
Reference, don't paste
Your .env holds vauly:// references. Nothing in it can leak.
DATABASE_URL=vauly://itm_7Gk2qXb9 - 2
Run through vauly
Values go straight into the process, masked in its output.
vauly run -- bun test api - 3
A person says yes
Each new item waits for someone to allow it, once or for an hour. Pause an agent anytime.
- How agents work →
Fills where you sign in.Saves what you type.
- Choose vauly's mark in any login field to fill.
- Sign in somewhere new and it offers to save.
- The site can't read the menu. It's vauly's own frame.

- Linearalex@acme.exampleFill
- Linear (admin)ops@acme.example
Forgot your password?
Small things,done properly.
- 2weak passwordsReview
- 1used in two placesReview
- 3seen by someone who leftReview
Password health
Weak, reused and exposed passwords, worked out on your device.
Two-step login
A code from your phone, with recovery codes for a bad day.
Share links
Send one item to anyone. It expires, and the server can't open it.
- Alex copied the password for GitHub2m
- Claude Code used Postgres · staging8m
- Riley revealed Office Wi-Fi1h
- Jordan shared Figma3h
- Alex removed Sam from Engineering1d
Every use, on the record
Reveals, copies, shares and agent runs, in one activity log.
Hard to lose things
Thirty days to undo a delete. Old passwords stay under Earlier.
Move in from anywhere
Import from 1Password, Bitwarden, LastPass and your browser. Export any time.
Light and dark, ⌘K everywhere, and it installs on your phone.
The server can't read it.Not even the names.
Every item is sealed in your browser before it's saved. Your master password is the only key, and only you hold it.
- Master passwordNever leaves your devicePBKDF2-SHA256 · 600,000 rounds
- Master keySplit by HKDF into a sign-in key and a wrap keyWrap key opens
- Your private keyECDH P-256Opens what teammates shared
- Vault keyAES-256-GCM, one per vaultWraps
- Item keyAES-256-GCM, one per item
Encrypted, out of the server's reach
- Item names, usernames and passwords
- Notes, websites and one-time code secrets
- Vault names
- Your private key and every vault key
What the server does see
- Emails, names and roles
- Who can open which vault
- When items are used
Open source and small enough to read, but not independently audited yet.Read the model and its limits →
One click.On your Cloudflare.
No vauly cloud, no account with us. A small team fits in Cloudflare's free plan.
- 1Deploy to CloudflareConnect GitHub. Cloudflare copies vauly into a repository of yours and builds it.
- 2Choose a setup codeOnly you know it, so nobody claims your vauly before you do.
- 3Claim itOpen the setup link, create your workspace, invite your team.
- 4Stay currentRun Update vauly in your repository's Actions. Cloudflare deploys it.
Is vauly free?
Yes. It's open source under AGPL-3.0. You only pay for your own Cloudflare account, and a small team usually fits in the free plan.
Can anyone at vauly see our data?
There's no one to ask. There is no vauly cloud: it runs on your Cloudflare account, and even that server only ever stores ciphertext.
What if I forget my master password?
Nobody can reset it, not even an admin. It's the only key to your items. An admin can invite you again so you start over, which is why vauly asks you to print an Emergency Kit.
What happens when someone leaves?
Remove them and their copies of the vault keys are deleted. vauly then lists every item they could open, so you can change what matters.
Can we move from 1Password or Bitwarden?
Yes. Import their CSV exports, or Chrome's, Firefox's and Safari's. You can download a full backup any time, too.
Has it been audited?
Not yet. The design is small and documented, and every line of code is open to read.
Own your secrets.Deploy in one click.
Free, open source, and running on your own Cloudflare.